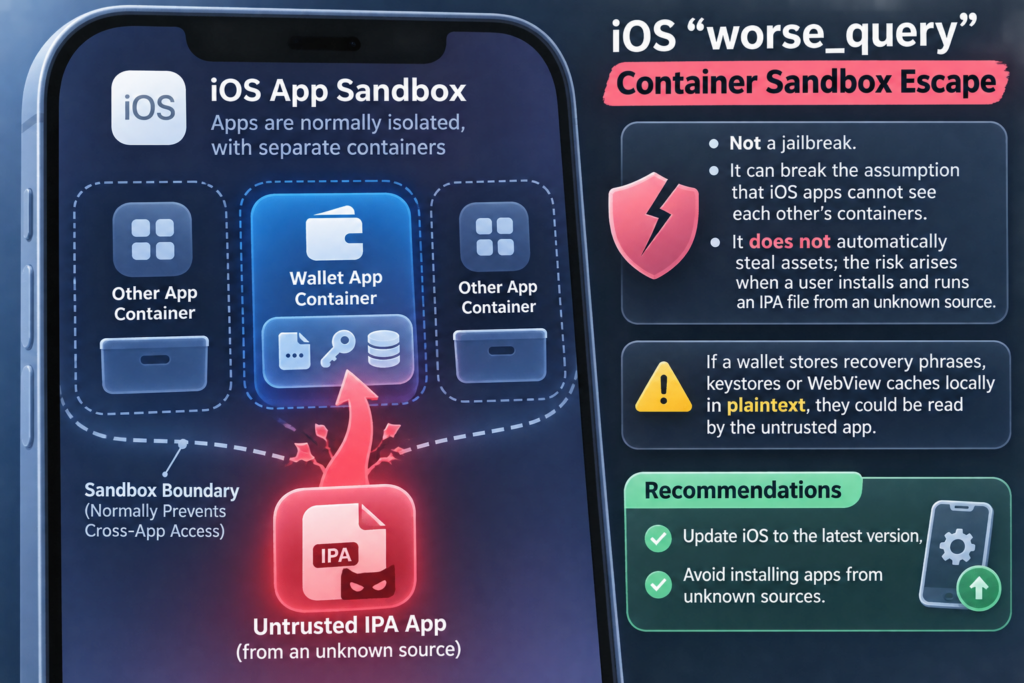
If you use an iOS wallet, the concern in this warning is not that the vulnerability automatically steals assets. It is what an untrusted app might be able to read if you install and run it.
In a PANews report published November 10, 2026, at 11:01 a.m. UTC+8, SlowMist chief information security officer 23pds described worse_query as a container sandbox escape, not a jailbreak. According to 23pds, it can break the assumption that iOS apps cannot see one another’s containers.
23pds said the risk arises when a user installs and runs an IPA file from an unknown source. The app could then read other apps’ containers; wallet recovery phrases, keystores or WebView caches would be at risk of exposure if a wallet stores them locally in plaintext. The report does not say that assets were stolen.
The practical steps 23pds recommended were to update iOS to the latest version and avoid installing apps from unknown sources.
Source: panewslab.com (originally published 2026-11-10 11:01 UTC+8)