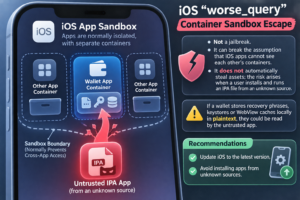
A wallet’s locally stored recovery data could be at risk if an untrusted app can read another app’s files. In a BlockBeats report published on November 10, 2026, SlowMist chief information security officer 23pds warned that the iOS vulnerability worse_query is a container sandbox escape, not a jailbreak, and may undermine data isolation between apps.
According to 23pds, the vulnerability does not steal assets on its own. The concern arises if a user installs and runs an IPA from an unknown source: a malicious app might then read other apps’ containers. Wallet data could be exposed if a wallet stores a recovery phrase, keystore or WebView cache locally in plaintext.
23pds advised users to update iOS to the latest version and avoid installing apps from unknown sources. The report described a potential exposure path, not a confirmed wallet theft.
Source: theblockbeats.info (originally published 2026-11-10 11:04 UTC+8)