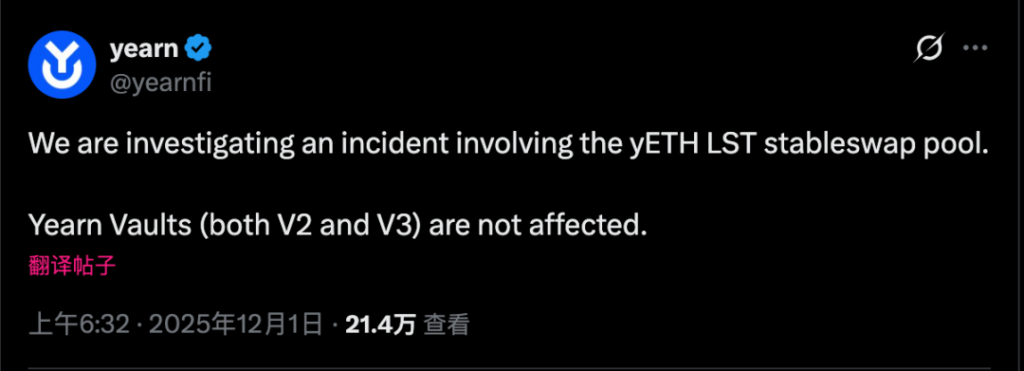
If you held yETH or supplied assets to its pool, the distinction in this incident is between a wallet compromise and a failure in the pool’s accounting. In an analysis published on December 4, 2025, SlowMist said an attacker exploited the Yearn yETH Weighted Stableswap Pool on December 1, with losses estimated at about $9 million. The report does not describe a compromise of users’ wallet keys.
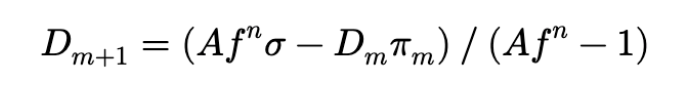
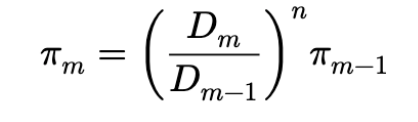
Where the calculation failed
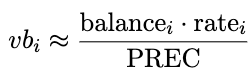
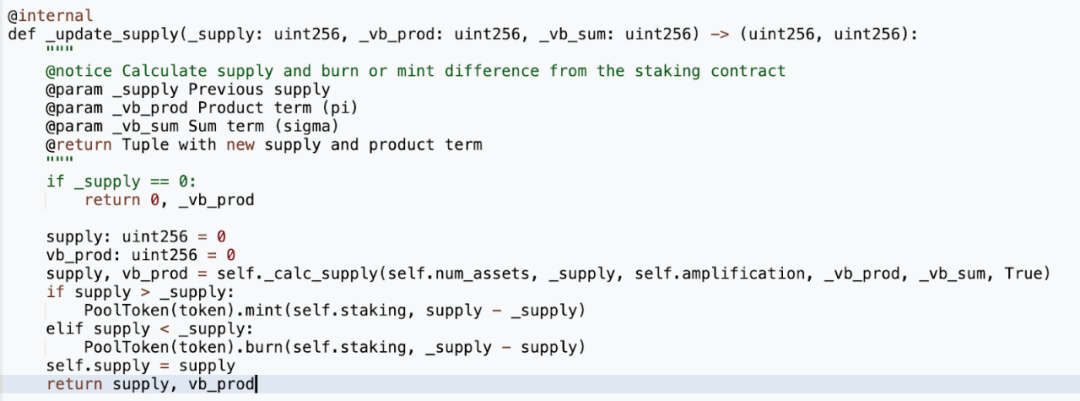
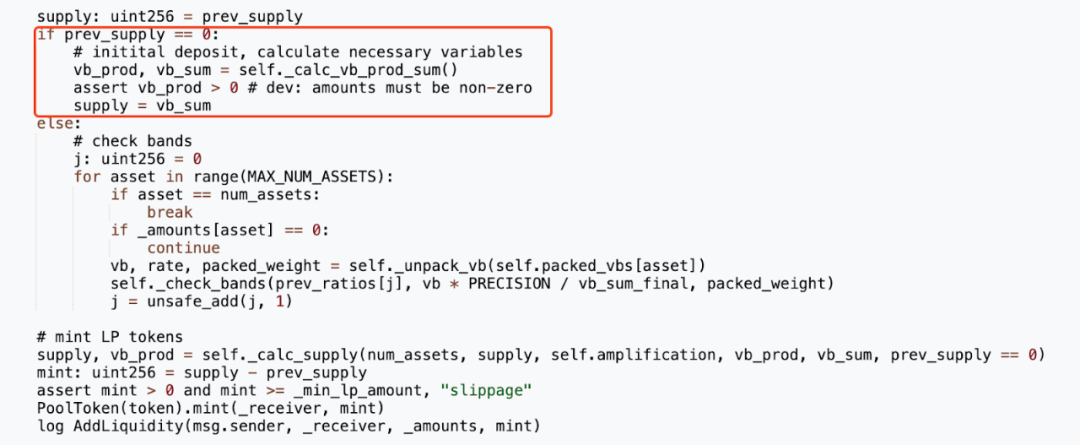
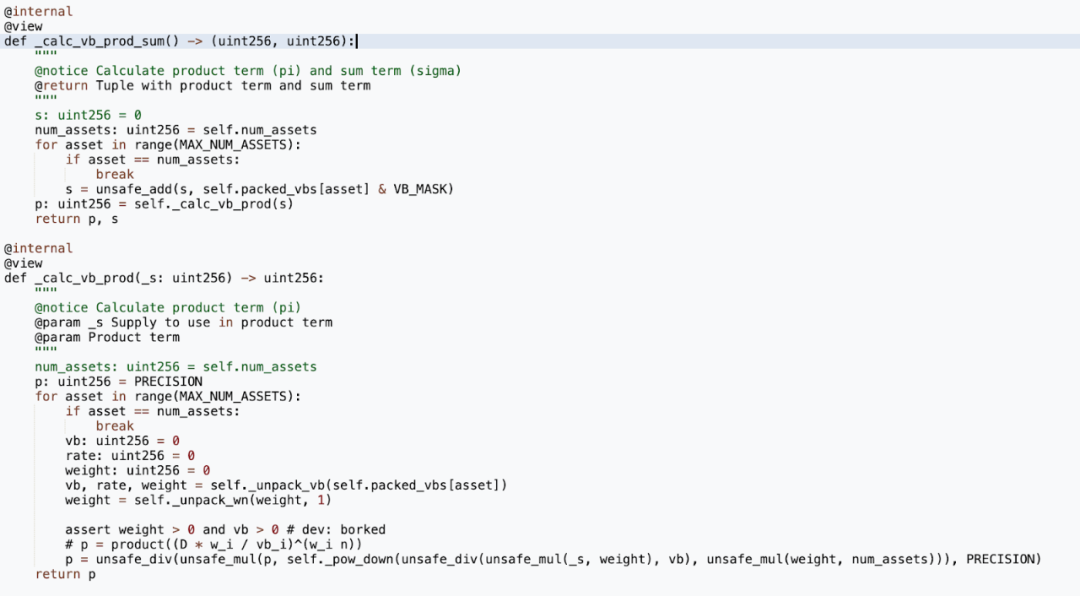
The pool holds eight Ethereum liquid-staking assets and tracks their rate-adjusted virtual balances. It also tracks a supply value, D, used when minting or burning yETH liquidity-provider tokens. According to SlowMist, the _calc_supply function used unchecked arithmetic while recalculating supply and the product of the virtual balances. Under the attacker’s chosen pool conditions, an unchecked subtraction underflowed; a subsequent calculation rounded the virtual-balance product to zero. That distorted the supply calculation and allowed more yETH to be minted than intended.
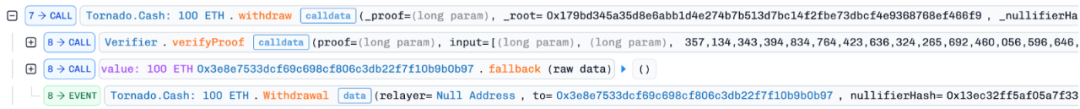
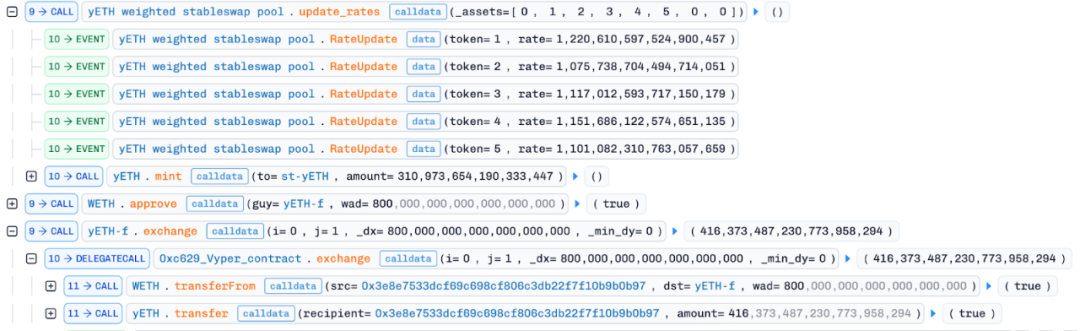
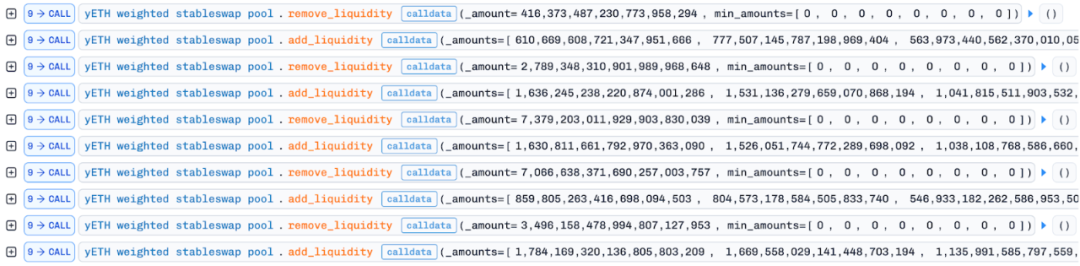
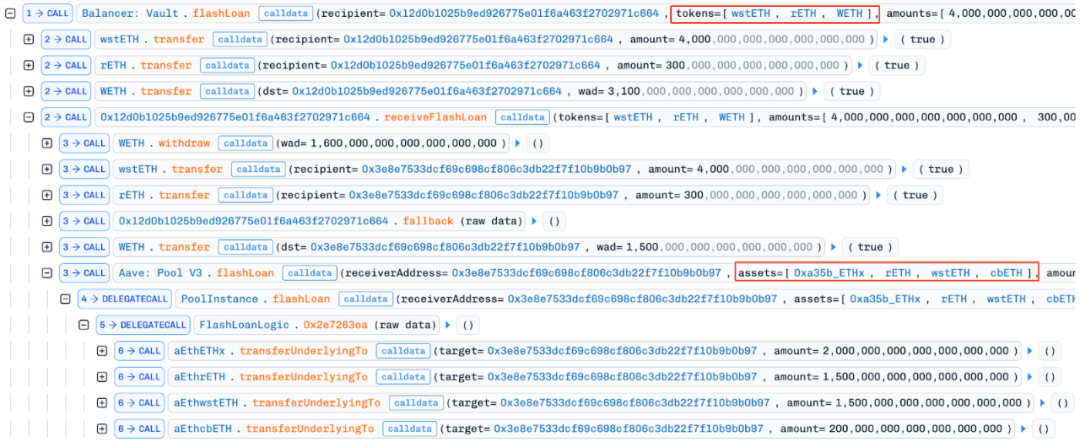
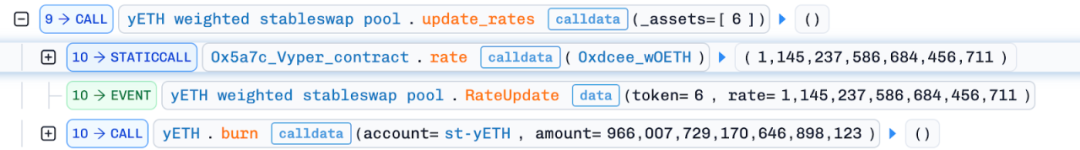
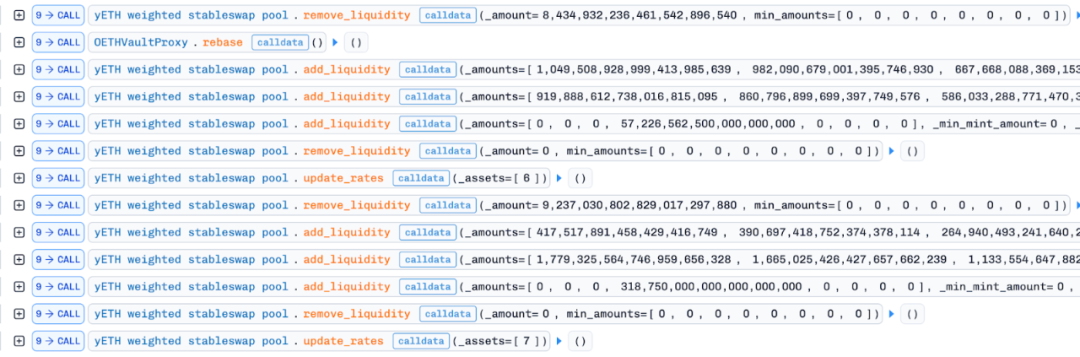
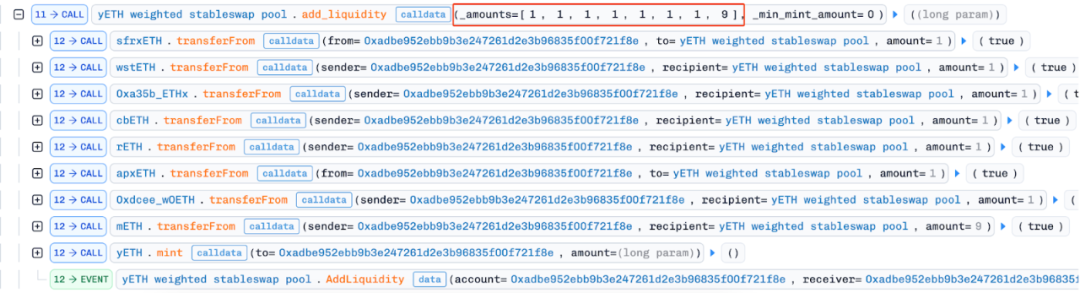
SlowMist’s transaction analysis says the attacker used flash-borrowed assets, updated rates and repeatedly removed and added liquidity, omitting certain assets when adding it back. After five such cycles, the virtual-balance product reached zero. The attacker then added cbETH on one side of the pool to mint additional yETH under the distorted accounting.
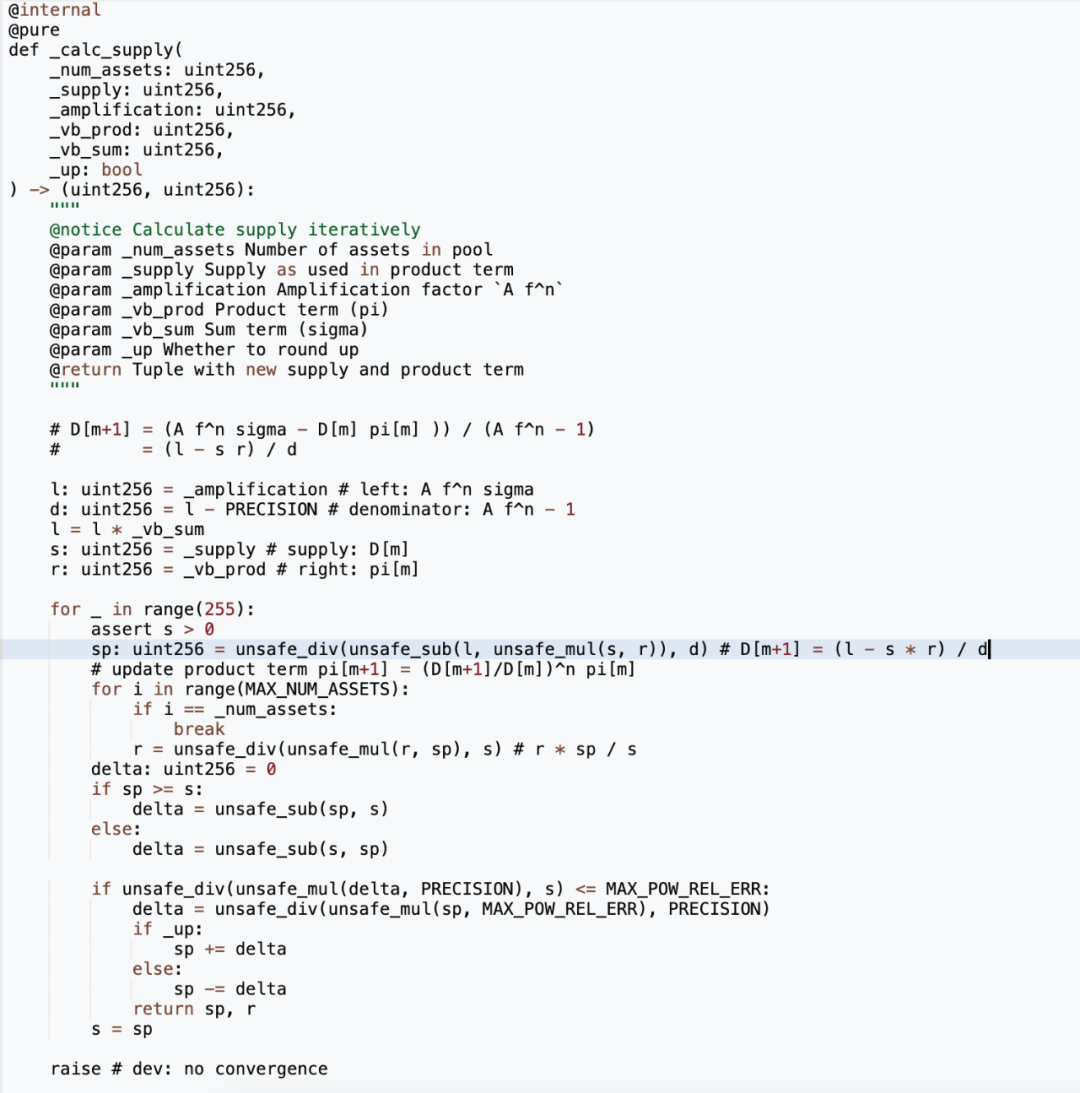
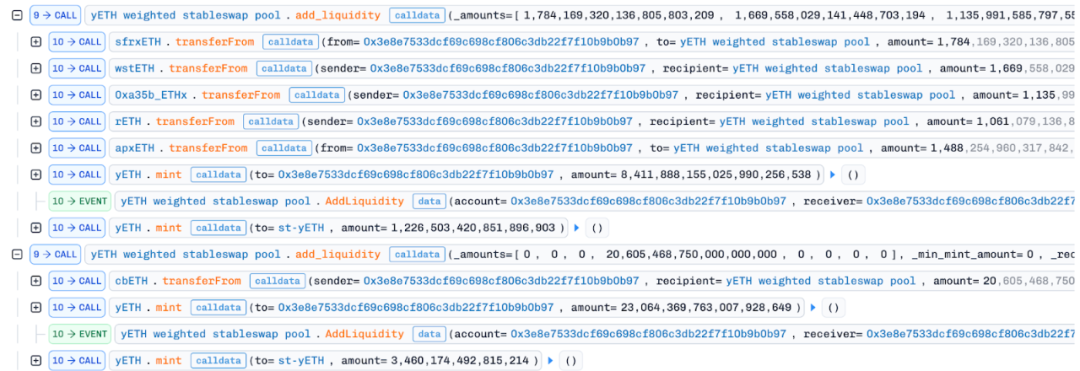
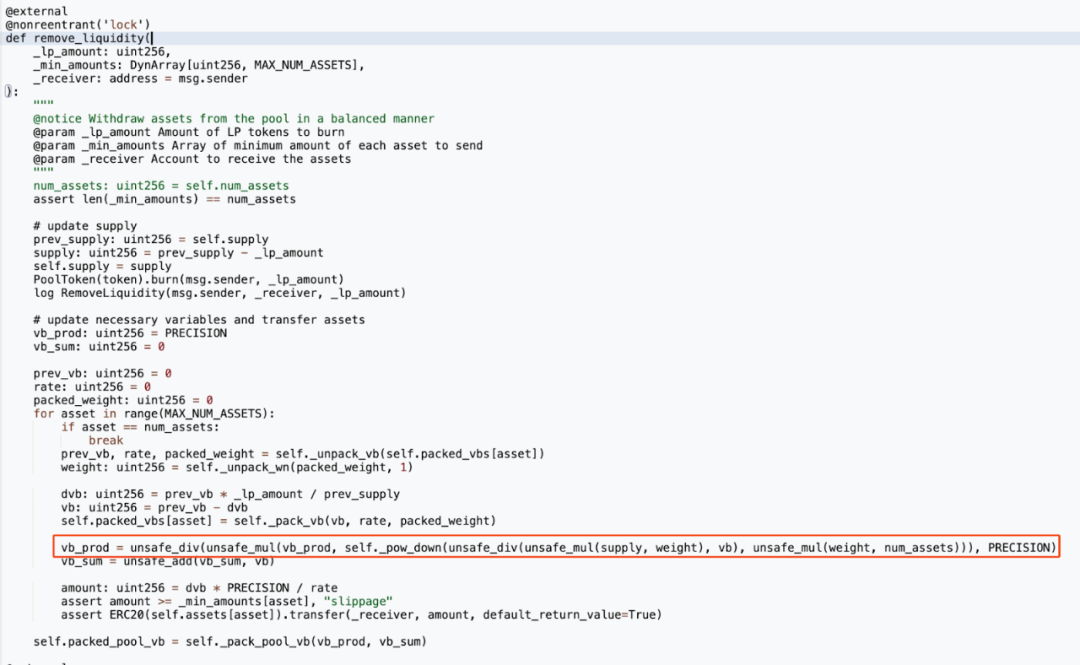
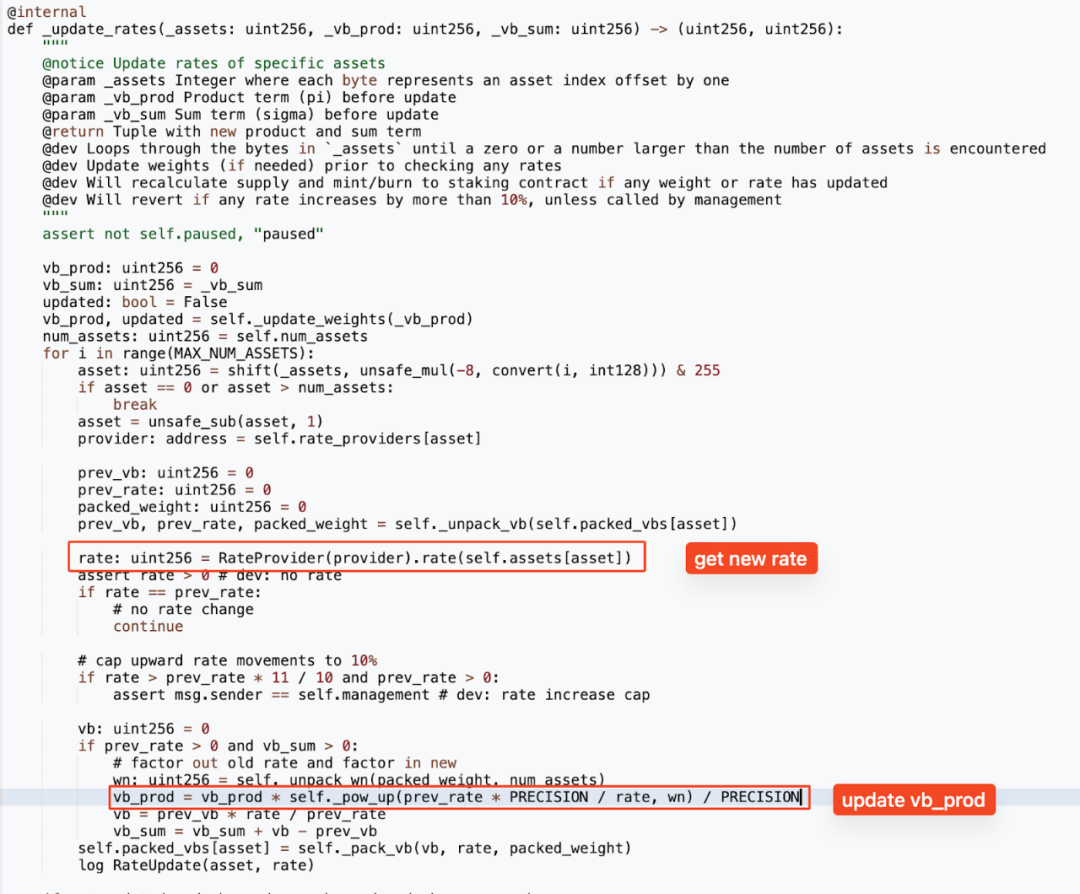
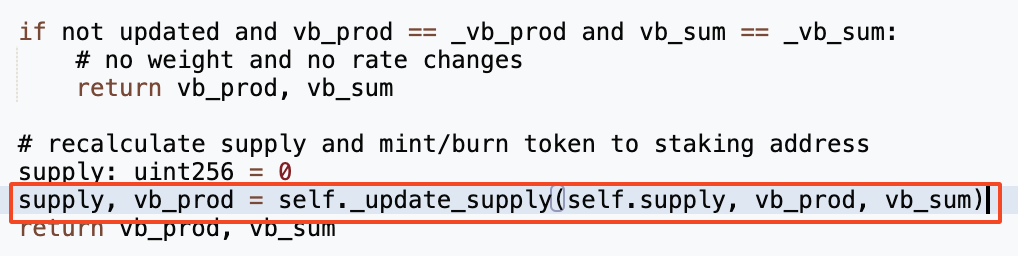
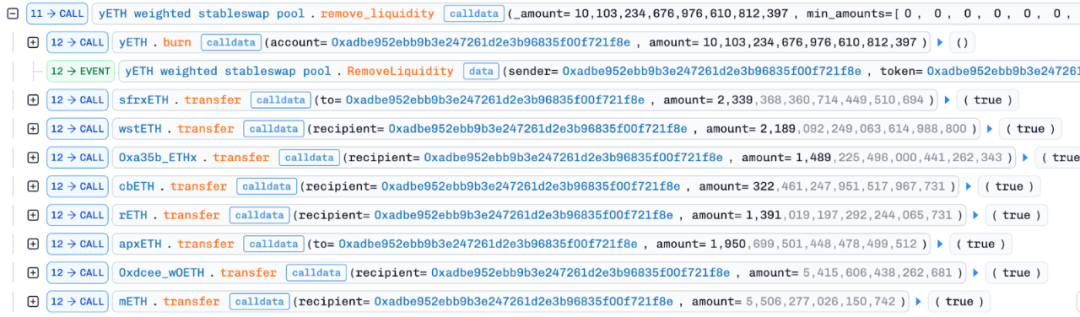
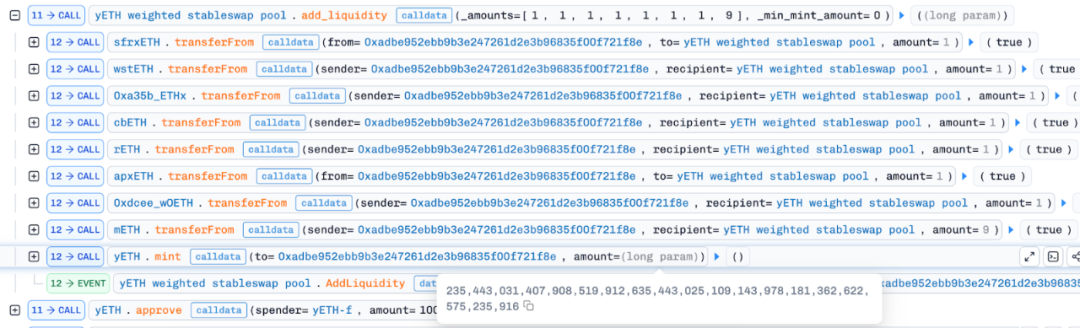
The report describes a second stage: a zero-amount liquidity removal recalculated the virtual-balance product to a nonzero value, and a wOETH rate update reduced the calculated supply. The attacker redeemed yETH minted under the earlier, inflated calculation and repeated the process until the pool was emptied. When small amounts of liquidity were added to the empty pool, SlowMist says a separate unchecked multiplication overflow in _calc_supply produced a calculated supply of approximately 2.354 × 10⁵⁶. The attacker sold yETH through an AMM and repaid the flash loans.
Funds traced and recovered
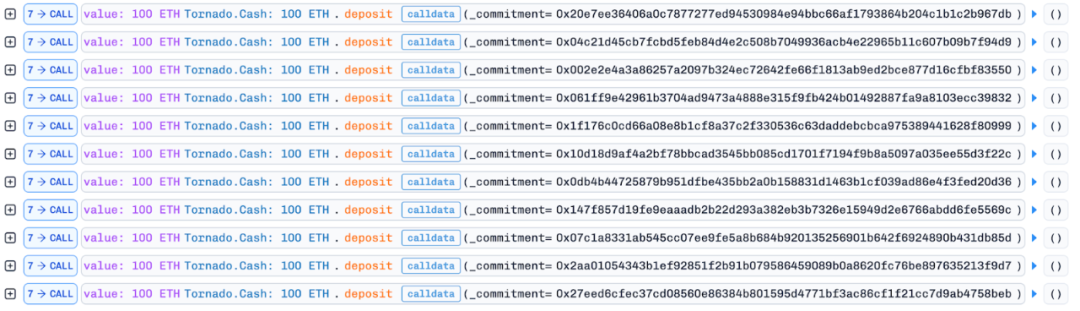
SlowMist’s MistTrack analysis estimates the attacker’s proceeds at about $9 million. It says the initial funding was a small amount of ETH from Railgun. After the attack began, 1,100 ETH was sent to Tornado Cash, of which 100 ETH was withdrawn for further exploitation. MistTrack also reported that assets worth roughly $6 million, including ETH and several liquid-staking tokens, were moved to one address.
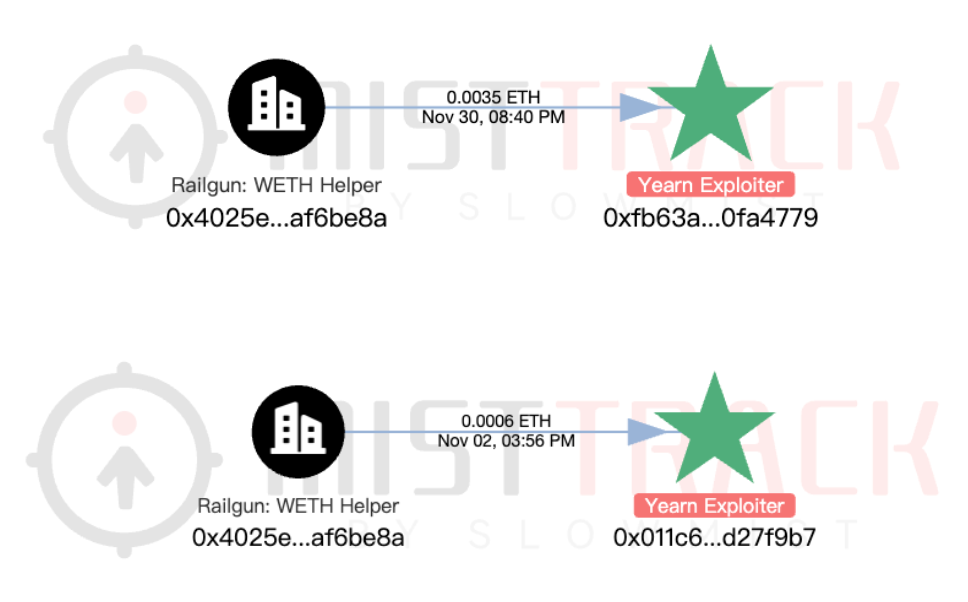
The report says Yearn subsequently recovered $2.4 million by burning 857.48 pxETH held by the attacker; the tokens were reminted and returned to a Redacted Cartel multisignature wallet. That reported recovery should not be confused with the estimated total loss or taken to mean all affected funds were recovered.
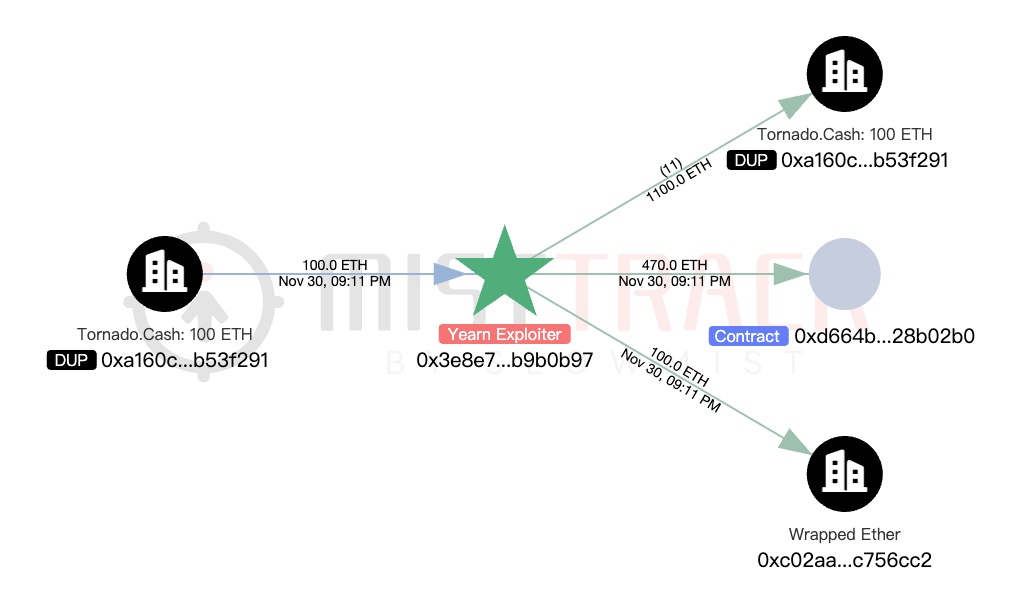
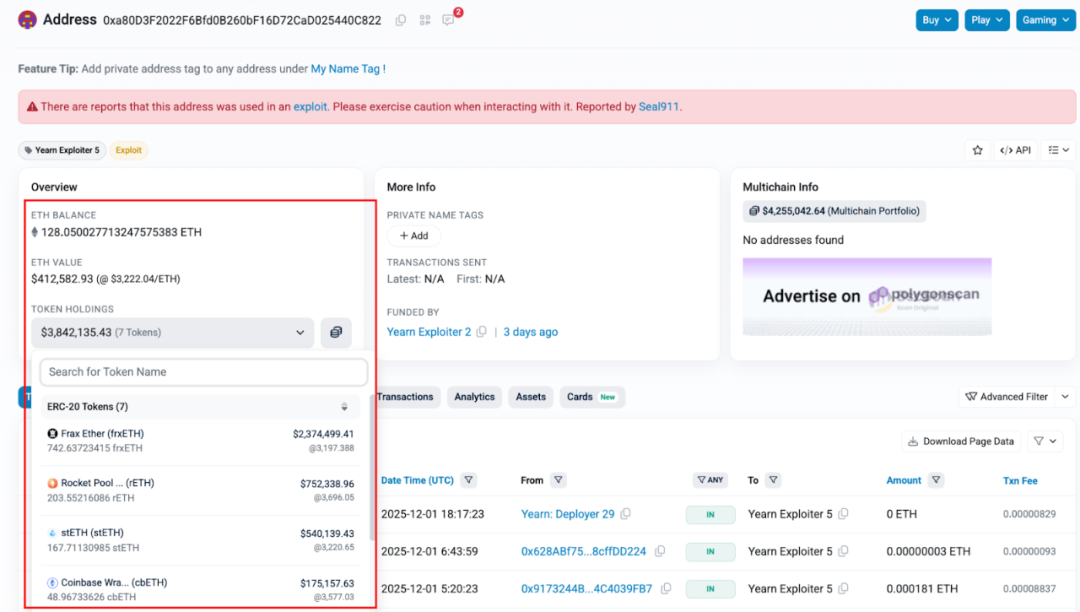
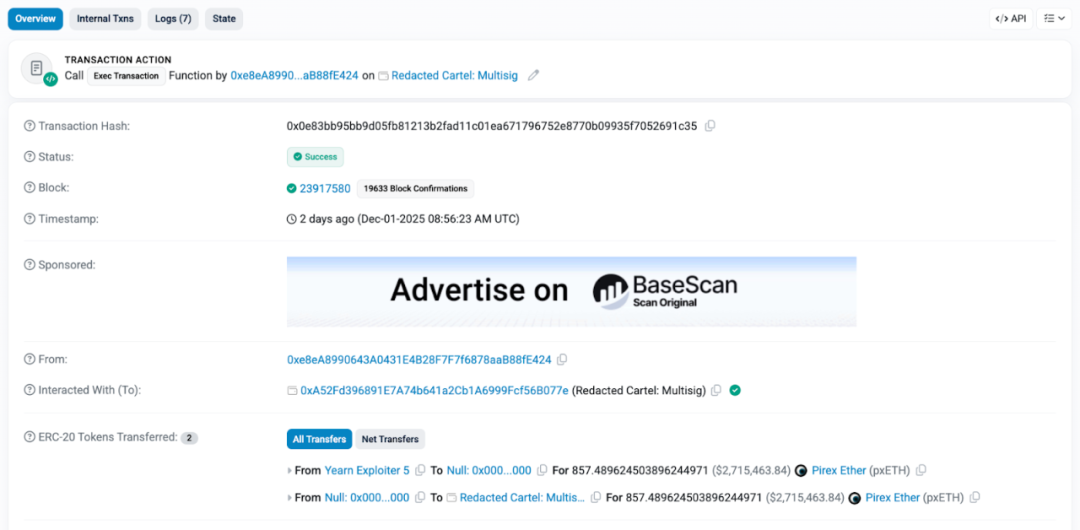
For holders, the practical boundary illustrated here is that control of wallet keys does not protect assets from faulty accounting in a protocol where those assets are deposited. SlowMist’s recommendation to developers and auditors was to test extreme conditions and boundary cases and use checked arithmetic for critical calculations.