Holding assets in a multisig wallet still depends on people understanding what they sign. In an article published on June 5, 2026, the author describes a “blind signing” problem: signers may be unable to independently verify a transaction’s actual contents, even when the required signatures are collected.
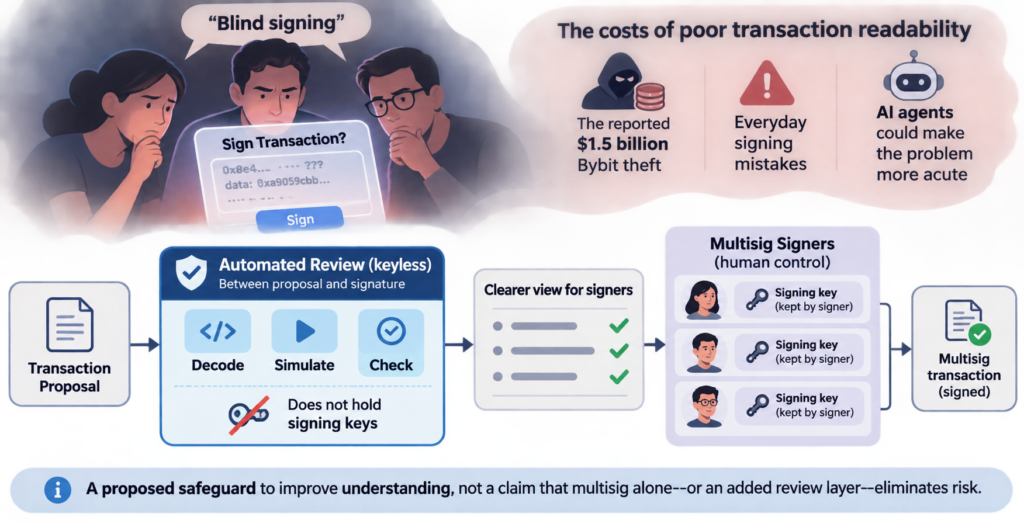
The article uses the reported $1.5 billion Bybit theft to illustrate its argument that a multisig process can operate as designed while signers authorize a malicious transaction they cannot readily read. It also identifies everyday signing mistakes as a cost of poor transaction readability and warns that AI agents could make the problem more acute.
The proposed safeguard is an automated review step between proposal and signature. It would decode, simulate and check a transaction without holding signing keys, so people retain signing control while getting a clearer view of what they are approving. That is a proposed approach, not a claim that multisig alone—or an added review layer—eliminates risk.