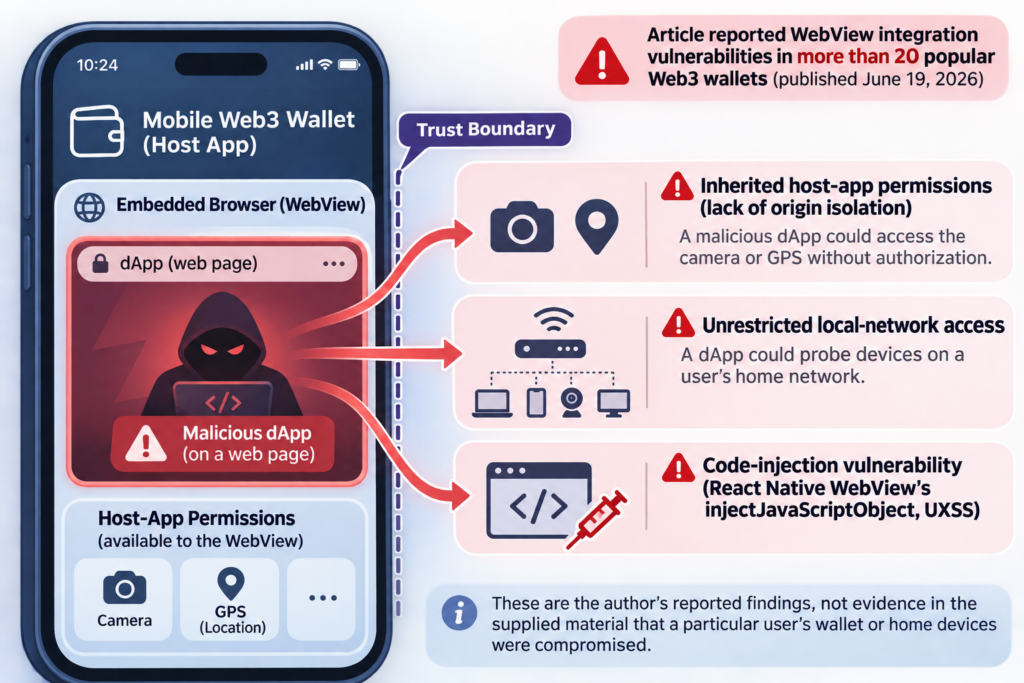
When a mobile wallet opens a dApp inside an embedded browser, what can that page reach? In an article published on June 19, 2026, the author reported WebView integration vulnerabilities across more than 20 popular Web3 wallets. The article included exploitation examples and suggested fixes, but the supplied summary does not identify the affected wallets or describe the fixes.
The author described three issues: WebViews inheriting host-app permissions without adequate separation between page origins, which could let a malicious dApp access the camera or GPS without authorization; unrestricted local-network access that could let a dApp probe devices on a user’s home network; and a code-injection vulnerability involving React Native WebView’s injectJavaScriptObject (UXSS).
For holders, the practical concern is the boundary between a dApp page and the wallet app hosting it. These are the author’s reported findings, not evidence in the supplied material that a particular user’s wallet or home devices were compromised.