If you keep wallet credentials on an iPhone, Binance’s November 10, 2026 warning is a reason to check your device and apps—not evidence that your funds have been stolen. At the time of the original report, there were no confirmed reports of crypto theft using the flaw.
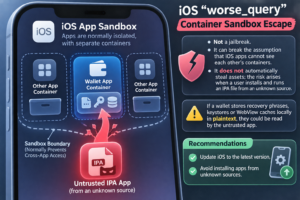
Binance said a vulnerability called worse_query could allow a malicious app to read local files belonging to other apps, potentially exposing seed phrases, private keys or login credentials. Its warning named iOS 26.7.1, 27.0.1 and 27.2 and described the issue as affecting iOS, not just Binance. Ordinarily, iPhone apps run in separate sandboxes that prevent this kind of file access.
A researcher using the name forcequitOS published worse_query as a proof of concept. The repository describes it as a sandbox escape affecting iOS 26.0 through 26.7.2 and iOS 27.2, but says it “isn’t useful by itself.” Those version ranges are the researcher’s description; they are not identical to the versions Binance named.
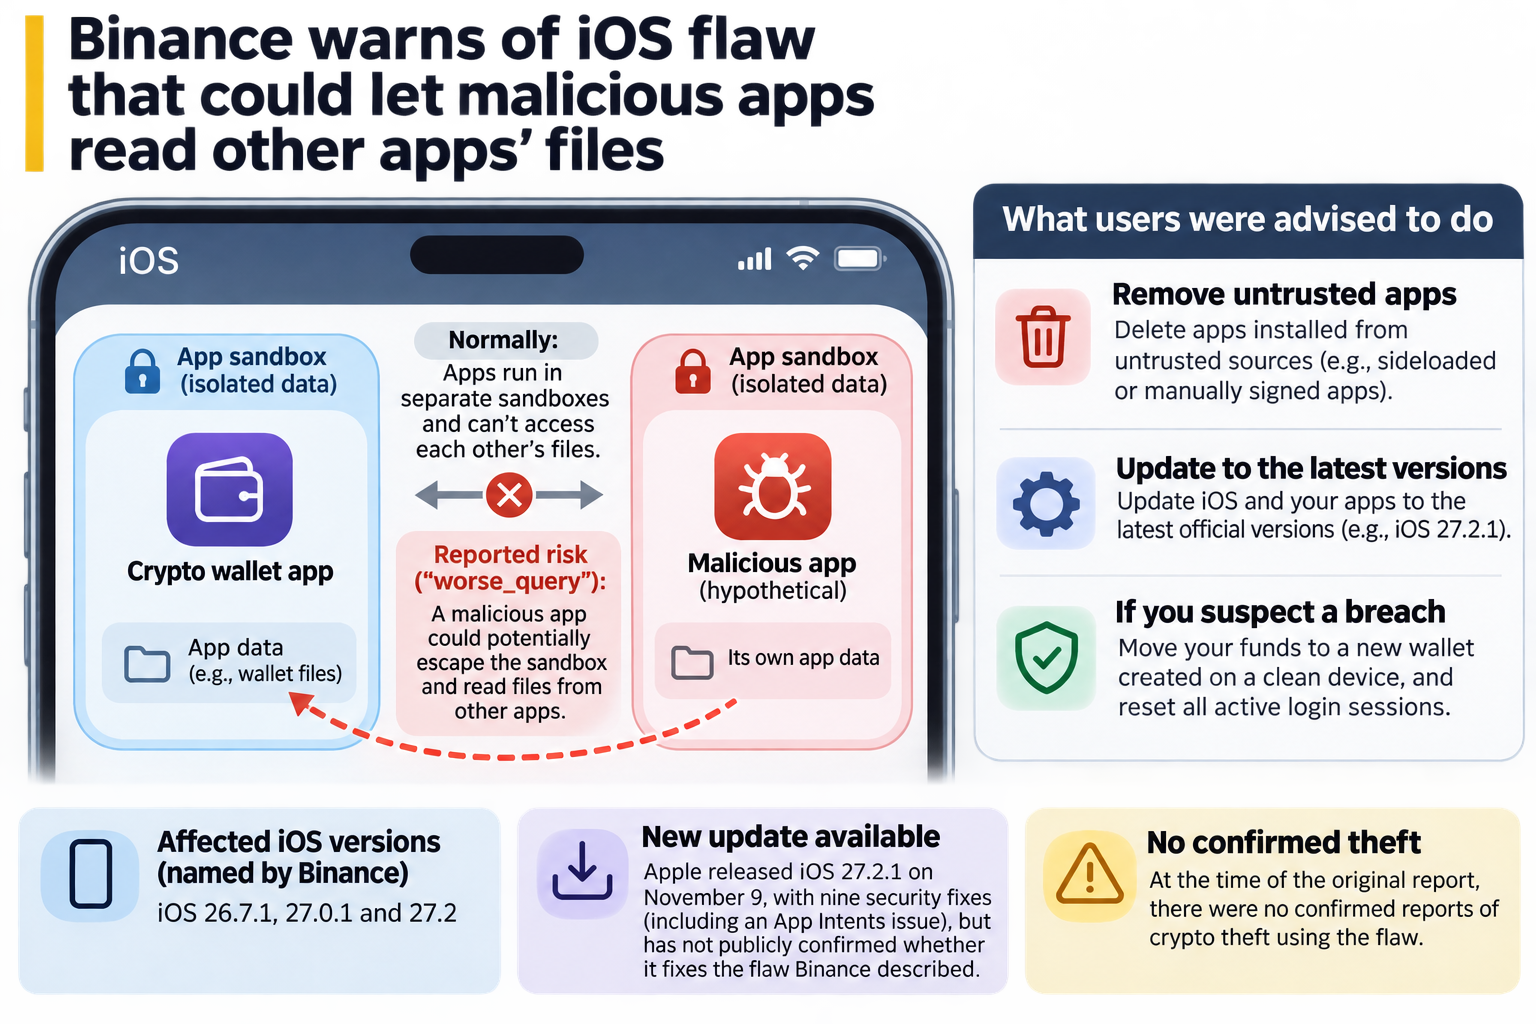
What users were advised to do: Binance urged users to remove apps installed from untrusted sources and update iOS and their apps to the latest official versions. For anyone who suspects a breach, it advised moving funds to a new wallet created on a clean device and resetting active login sessions.
Apple released iOS 27.2.1 on November 9. Its security notes listed nine fixes, including an App Intents issue that could let an app access sensitive user data, but did not name worse_query or its researcher. Apple had not publicly confirmed whether the update fixed the flaw Binance described. SlowMist chief information security officer 23pds said the update would block worse_query and urged users to install it; that assessment should not be mistaken for Apple’s confirmation.
Source: decrypt.co (originally published 2026-11-10 20:45 UTC+8)