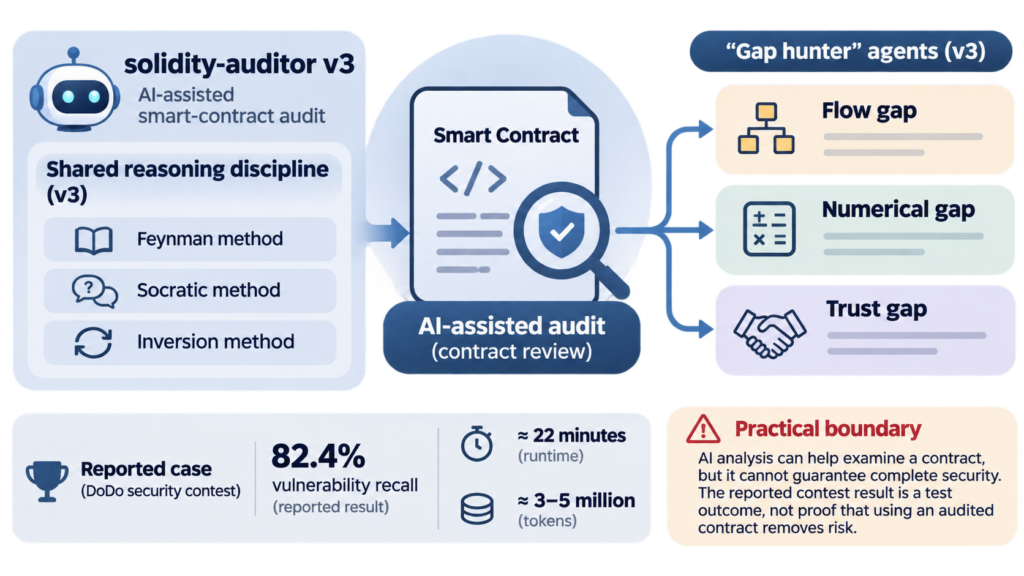
For anyone relying on a smart-contract audit before holding assets in a protocol, the key question is what the review might miss. An article published on June 5, 2026, presents solidity-auditor v3 as an AI-assisted auditing tool and reports 82.4% vulnerability recall in a DoDo security-contest case. That is the article’s reported result, not a guarantee that the tool will find every vulnerability in another contract.
The article describes two changes in v3. One is a shared reasoning discipline using Feynman, Socratic and Inversion methods. The other is a set of “gap hunter” agents focused on flow, numerical and trust gaps. In its comparison with other open-source tools, the article reports that v3 led on recall, with a runtime of about 22 minutes and token use of roughly 3–5 million.
The practical boundary is straightforward: AI analysis can help examine a contract, but the article cautions that it cannot guarantee complete security. The reported contest result should be read as a test outcome, not as proof that deploying or using an audited contract removes risk.